

IT & Cybersecurity Solutions for Louisiana Businesses
One local expert for your network, your security, and your IT. We protect what you have, build what you need, and bring in trusted partners for the rest, so you never have to figure it out alone.
What We Do
Cybersecurity and IT solutions for small businesses and homeowners across the Northshore and Greater New Orleans.
Networks & Wi-Fi
Clean, documented installs and Wi-Fi built for coverage, speed, and security from day one.
Cybersecurity
It all starts at the network. We find the gaps and close them, and bring in specialists for penetration testing, threat detection and response, and security leadership when you need more.
IT Solutions & Support
Fast troubleshooting when something breaks, plus the right internet, cloud backup, and business phone providers when you need them, with one point of contact.
Our Methodology
See how we design, implement, and secure your IT infrastructure with proven, industry-standard practices.
1. Scope & Documentation
We start every project by scoping exactly what you need, then map and document your entire network in a detailed plan for you to review before we deploy any changes.
2. VLAN Segmentation
We isolate critical devices and segment your network into VLANs to contain potential threats and protect sensitive data.
Swipe the diagram sideways · tap a VLAN to focus it
3. Firewall Configuration
We design and implement firewall rules based on the principle of least privilege, securing your perimeter against unauthorized access.
Firewall methodology — how a rule earns its place
The order the work happens in, and what the finished ruleset looks like.
Inventory first
Every device on the network, and what it legitimately needs to reach. You cannot write rules for traffic you have not identified.
Start at default deny
The baseline is that nothing is allowed. Rules are exceptions you argue for, not defaults you inherit from the box.
Open the service, not the network
Staff get the file server. Not everything else that happens to sit beside it. The less a device can reach, the less it can damage if it gets infected.
Document the reason
Every rule carries why it exists. A rule nobody can justify is a rule that gets removed at the next review, not grandfathered in.
| SOURCE | DESTINATION | SERVICE | ACTION | WHY |
|---|---|---|---|---|
| Staff | Servers | SMB (v3), HTTPS | ALLOW | Staff need their shared files. Being on the network is not enough — your group decides which folders open. |
| Staff | Management | — | DENY | Nobody should be able to change the firewall from a regular laptop. |
| POS | Payment processor | HTTPS | ALLOW | A register only needs to reach the card company. |
| POS | Any other VLAN | — | DENY | A register has no reason to touch anything else. |
| IoT | Internet | HTTPS, NTP | ALLOW | Smart devices get updates and the clock. Nothing else. |
| IoT | Servers, Staff, POS | — | DENY | A smart TV should never reach your files or your registers. |
| Guest | Internet | Web only | ALLOW | Visitors get Wi-Fi, not your network. |
| Any | Any | Any | DENY | Everything not listed above is blocked. That is the default, not the exception. |
Everything not listed above is blocked by default — the last rule is what is really doing the work. And getting on the network is not the same as getting access: a staff laptop can reach the file server, but which folders open is decided by who the person is.
4. WiFi Optimization
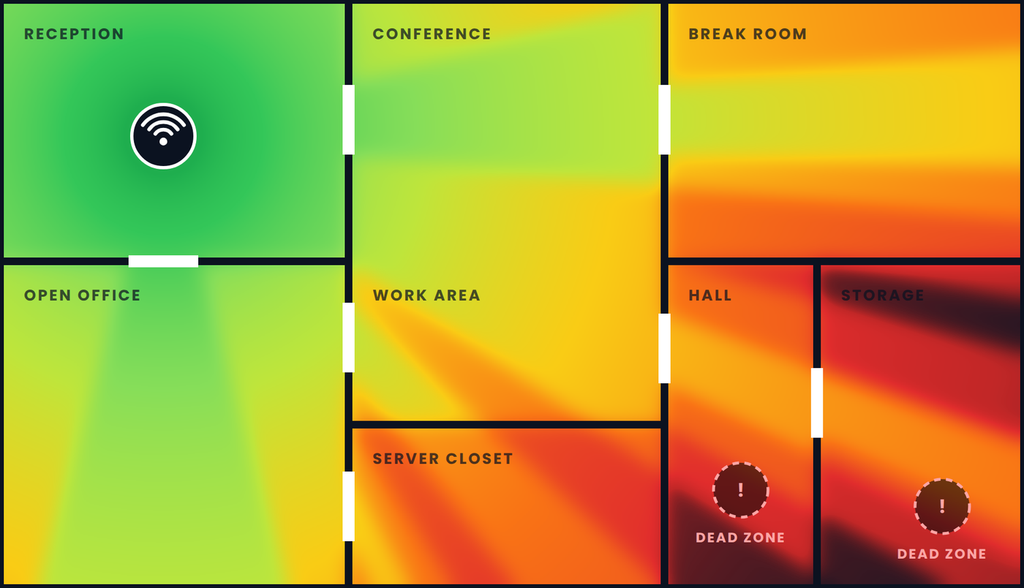
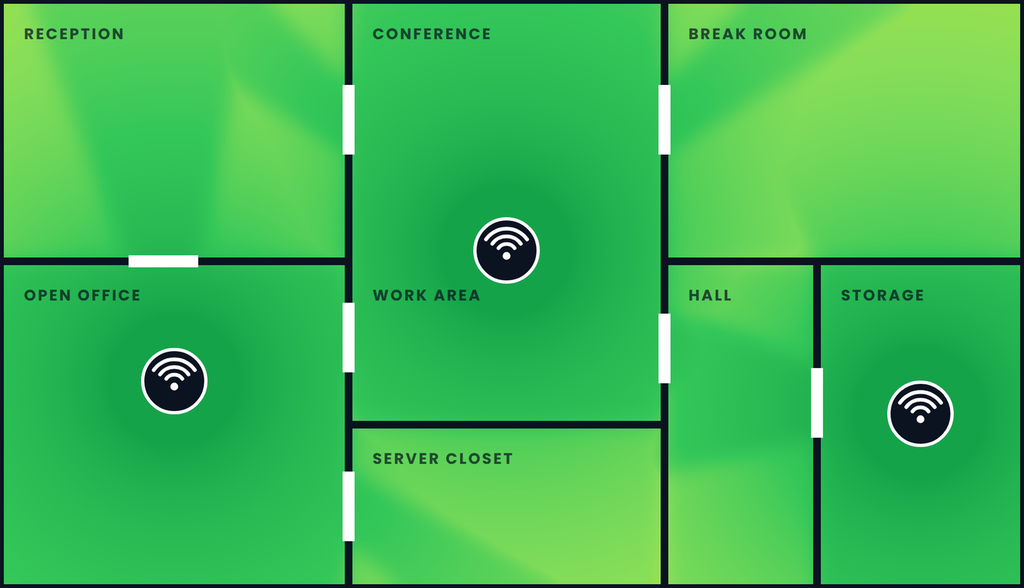
We analyze and optimize wireless coverage using precise heatmap analysis to ensure seamless connectivity throughout your facility.
One router vs. three placed access points
Same building, same walls. Drag the handle to see what changes.
Your Local Cybersecurity and IT Partner
Founded by a Louisiana Army National Guard IT Specialist, DeF-Sec brings military discipline to protecting small businesses and homeowners across the Northshore and Greater New Orleans. Tell us what worries you about your network, and we’ll take it from there.